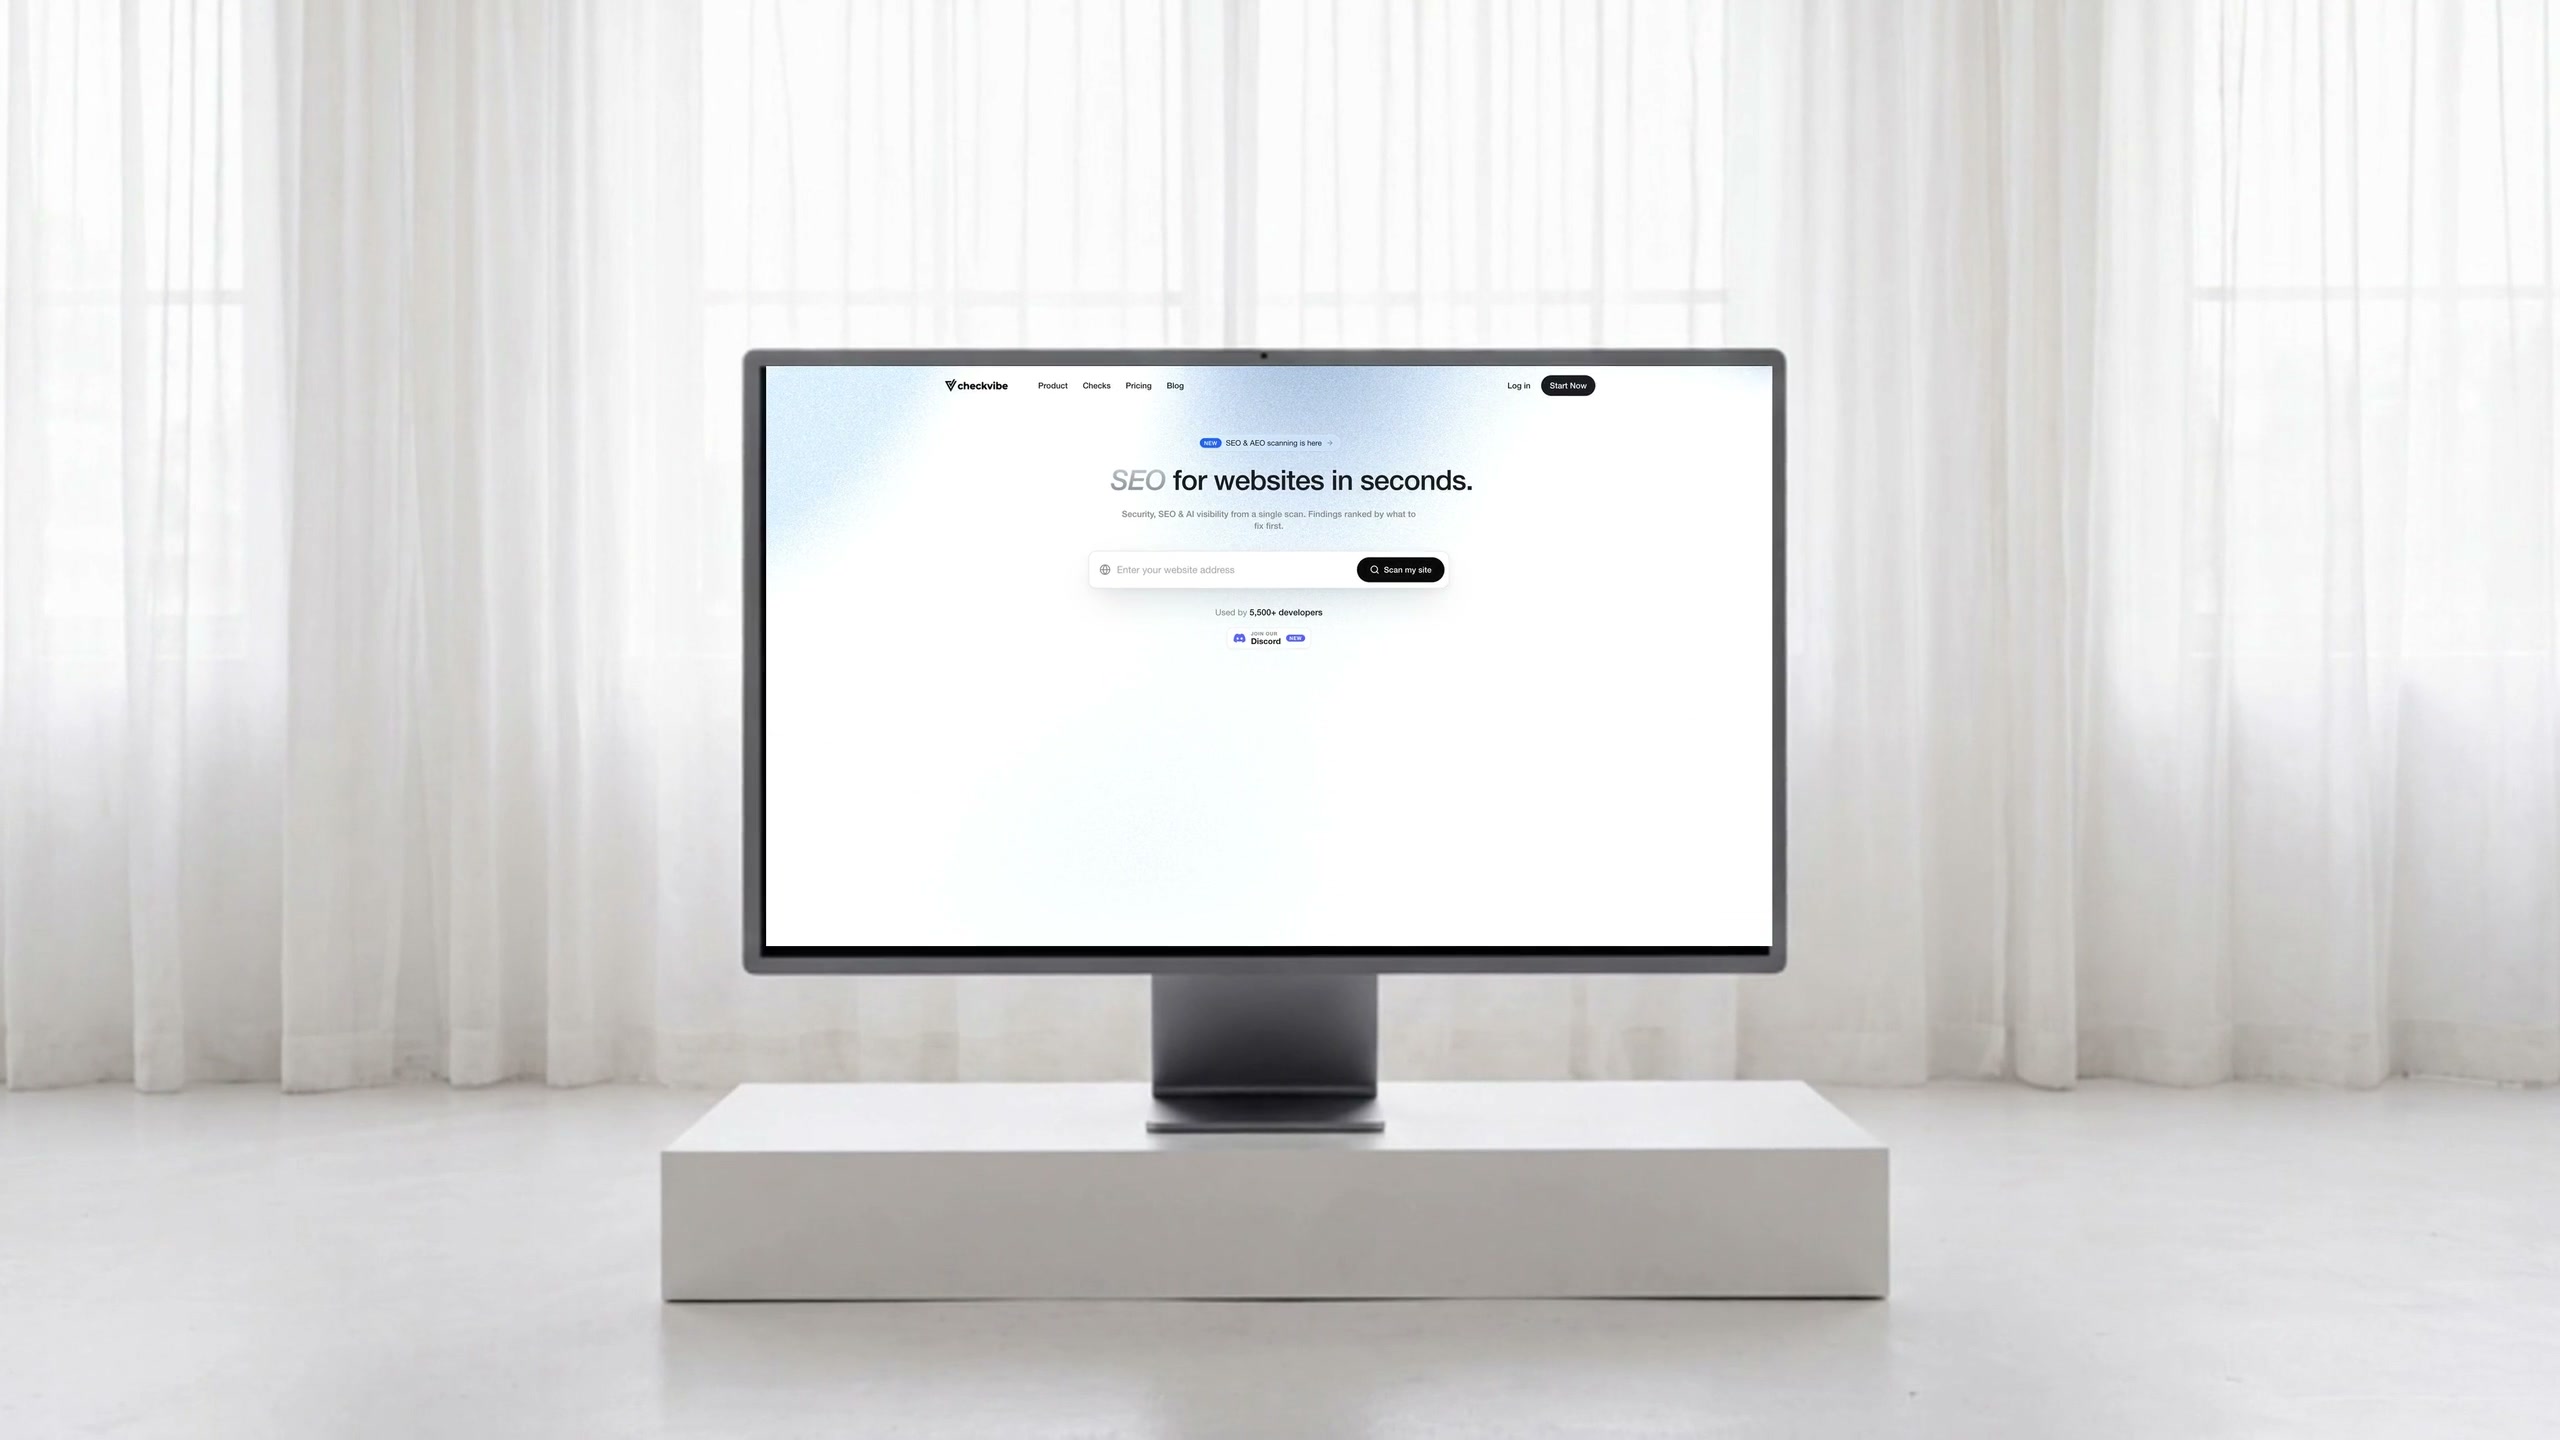
Secure everything you build, ship and run
Scan your live app, code, pull requests and cloud. Each finding with a fix.
Used by 7,000+ developers
Join ourDiscordNewScan your live app, code, pull requests and cloud. Each finding with a fix.
Used by 7,000+ developers
Join ourDiscordNew

 Cursor
 Windsurf
 VS Code
 Codex

 Copilot
Every finding ranked by impact.
Point it at your live app — production, staging or an AI-built prototype. Every check runs in parallel and comes back ranked, with a fix.
Link your GitHub repos and Supabase backend — CheckVibe scans the code and config too, not just the live app.
Plug CheckVibe into Claude, Cursor or any agent over MCP — or call the REST API directly.
Every finding becomes a copy-paste prompt — hand it to Cursor, Claude or any agent and it fixes itself.
Live threat detection, PR reviews and uptime monitoring — all in one dashboard.
Every layer — live app, code, dependencies, secrets, cloud and containers.
Watch it. Defend it.
A clean report is just the start. CheckVibe keeps watch on your live app and tells you the moment something goes wrong.
Watch real attacks hit your live app the moment they happen: credential stuffing, scraping, and injection probes, each with the attacker’s IP and an email alert within minutes.
60-second uptime probes with down-and-recovery alerts within minutes and a public status page. You hear it from us, not from an angry customer.
Live-app scans, repo scans and PR reviews, in one queue.
100+ live-app checks, SAST, dependency and secret scans, PR reviews and cloud config. Ranked by impact, each with a fix.
Open findings · 3 to fix
Scan the app your AI tools built, connect GitHub and Supabase for code and backend audits, and pull findings into Claude, Cursor or any MCP client.
One subscription. Fewer tabs open.
Every finding below lands in the same queue as your code and PR reviews.
Security use cases by team type.
Each pull request gets a check run and a comment on every new finding.
Security patches opened against your repo as reviewable pull requests.
SAST, dependency and secret scans across every repo you connect.
Assign, comment and track findings across every seat, with roles.
Real scans on real AI-built apps, in their words.
Cursor writes most of my code and I kind of just assume it works. I had no real way to tell if any of it was secure. Scan came back with four criticals.
The report is just the start.
Wire CheckVibe into the way you already work.
24 tools. Run scans and pull findings from Claude, Cursor or any MCP client.
Connect GitHub and scan every repo and pull request: SAST, secrets, dependencies.
CheckVibe re-checks your app on a schedule and emails you the moment something new turns up.
Every report as PDF and Markdown, built for handoffs and paper trails.
Registration runway, registrar locks, DNS resilience and certificate expiry — caught before they bite.
Every scan is kept. Watch the count come down as things get fixed.
Yes. Checks are read-only probes of what is already publicly reachable. Nothing is written, submitted or modified.
Every scan runs 100+ security checks (vulnerabilities, exposed secrets, headers, CORS, CSP) across your live app, plus code, dependency and secret scanning once you connect a repo.
No agent or SDK. Live-app checks run from outside, and the GitHub App adds code scanning and PR reviews.
Standalone checkers anyone can run without an account: a website security scan, an exposed API key checker, a Supabase RLS checker, and free SEO and AEO checkers. They are side tools; CheckVibe itself is a security platform.
Paid plans unlock the full findings with paste-ready fixes, continuous monitoring with alerts, scheduled re-scans and API access. Team plans add seats and roles, PR security reviews and AutoFix pull requests.